
Key Features
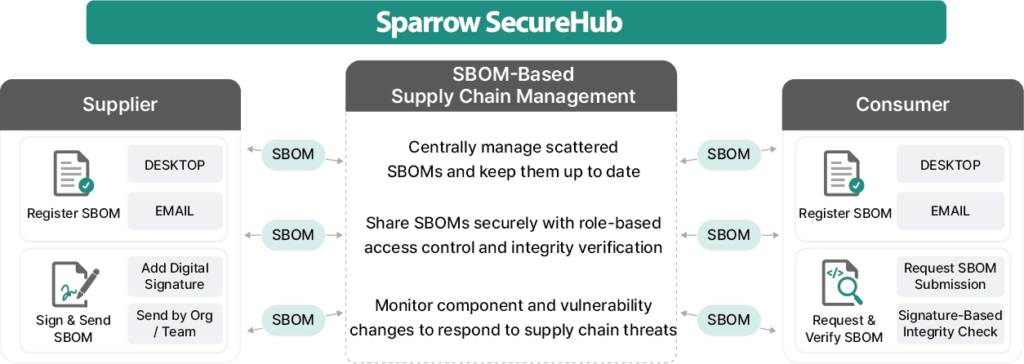
Centralized SBOM Management
SBOM Sharing and History Management
Signature-Based SBOM Tamper Protection
Software Supply Chain Security Management
Build a Supply Chain Security Framework by Securely Sharing and Centrally Managing SBOMs
FAQ
Yes. However, files generated by other tools cannot be verified for tampering, so they are registered with an ‘Unsigned’ status.
Yes. Integration depends on your product environment:
– Sparrow Enterprise: Requires version 2511.1 or later. Issue an access key in Sparrow SecureHub to configure the integration.
– Sparrow Cloud: Available with paid open source analysis plans. When exporting an SBOM, select ‘Export to Sparrow SecureHub’ and the signed file is registered automatically. See the User Guide for detailed setup instructions.
It currently uses Sigstore Cosign, which requires no separate encryption key management. Support for additional methods will be expanded over time.
To guarantee data integrity. There is a risk that someone could maliciously modify an SBOM or hide vulnerability information. A signature acts as a ‘digital seal,’ proving that the distributed SBOM is the unaltered original created by its author.
It supports the major standards CycloneDX, SPDX, and SWID. Supported versions and file extensions are as follows:
– CycloneDX 1.4 (.json, .xml)
– CycloneDX 1.5 (.json, .xml)
– CycloneDX 1.6 (.json, .xml)
– SPDX 2.2 (.spdx, .json, .xml)
– SPDX 2.3 (.spdx, .json, .xml)
– SPDX 3.0 (.jsonld)
– SWID (.swidtag)