
Open Source Analysis and Management Tool
A tool that identifies open source software licenses anddetects security vulnerabilities for efficient software supply chain management
A tool that identifies open source software licenses and detects security vulnerabilities for efficient software supply chain management
Sparrow
SCA
Where It Fits
Where It Fits
Generate SBOMs with VEX Information
Generate SBOMs that include VEX information to communicate whether vulnerabilities actually affect your software and what their remediation status is
Meet Global SBOM Requirements
Identify software components and generate SBOMs to meet supply chain requirements such as the EU Cyber Resilience Act (CRA), U.S. Executive Order 14028, and the FDA cybersecurity guidance
Identify software components and generate SBOMs to meet supply chain requirements such as the EU Cyber Resilience Act (CRA), U.S. Executive Order 14028, and the FDA cybersecurity guidance
Why Sparrow
Build Open Source Governance Through License and Vulnerability Management
Automatically identify the open source components in use and get vulnerability information along with license-specific notice obligations. CVSS, EPSS, and KEV data help you prioritize vulnerability response. Integrate with open source repositories and set and enforce intake policies to build an organization-wide governance framework for using open source safely.
Manage Software Supply Chain Risk, from Open Source AI Model Identification to SBOM Generation and Analysis
Automatically identify open source AI models, generate and analyze SBOMs in standard formats such as SPDX and CycloneDX, and use VEX information to verify whether vulnerabilities actually affect your software. Comply with software supply chain security requirements such as the FDA cybersecurity guidance, the EU Cyber Resilience Act (CRA), and U.S. Executive Order 14028, and gain transparency across the entire supply chain.
All-in-One Analysis from Source Code to Container Images
Analyze source code, binaries, and container images to manage and remediate vulnerabilities comprehensively. For source code, build analysis is also supported to precisely identify dependencies.
01
Build Open Source Governance Through License and Vulnerability Management
Automatically identify the open source components in use and get vulnerability information along with license-specific notice obligations. CVSS, EPSS, and KEV data help you prioritize vulnerability response. Integrate with open source repositories and set and enforce intake policies to build an organization-wide governance framework for using open source safely.
02
Manage Software Supply Chain Risk, from Open Source AI Model Identification to SBOM Generation and Analysis
Automatically identify open source AI models, generate and analyze SBOMs in standard formats such as SPDX and CycloneDX, and use VEX information to verify whether vulnerabilities actually affect your software. Comply with software supply chain security requirements such as the FDA cybersecurity guidance, the EU Cyber Resilience Act (CRA), and U.S. Executive Order 14028, and gain transparency across the entire supply chain.
03
All-in-One Analysis from Source Code to Container Images
Analyze source code, binaries, and container images to manage and remediate vulnerabilities comprehensively. For source code, build analysis is also supported to precisely identify dependencies.
Key Features
Detect open source license usage, security vulnerabilities, and manage them efficiently in one place.
Open Source Vulnerability Detection
OSS License Identification and SBOM Generation
Analysis of Diverse OSS Forms
Easy Integration with Software Development Processes
Convenient Result Review
Built for Multi-User Environments
Use Case
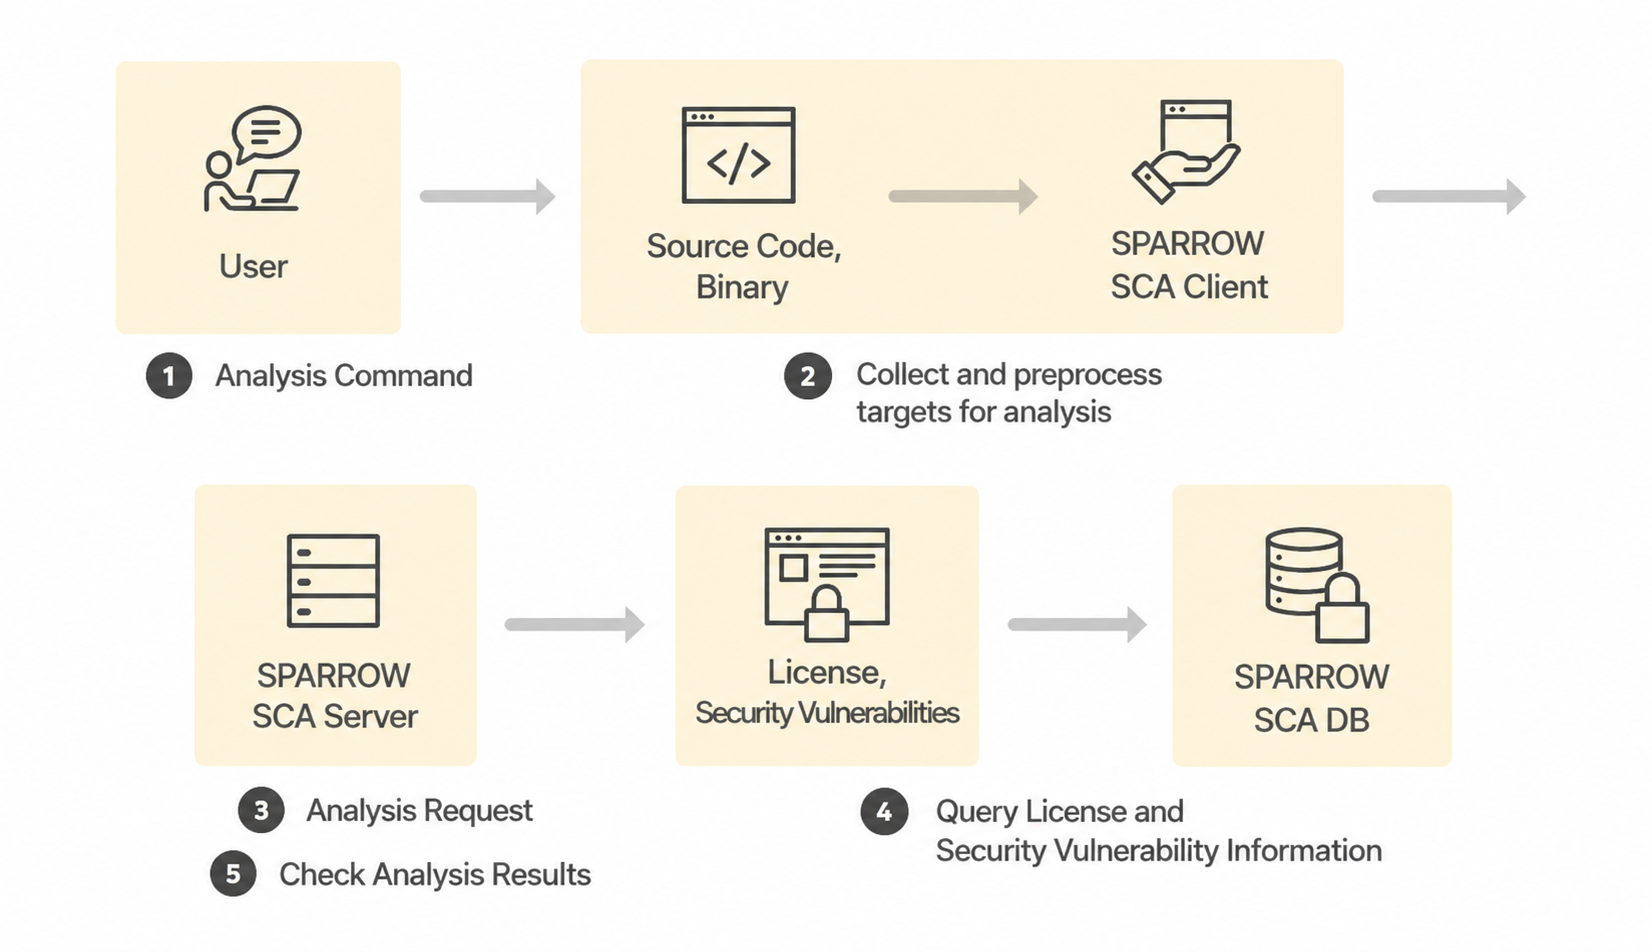
License Verification and Vulnerability Detection for Open Source in Any Form
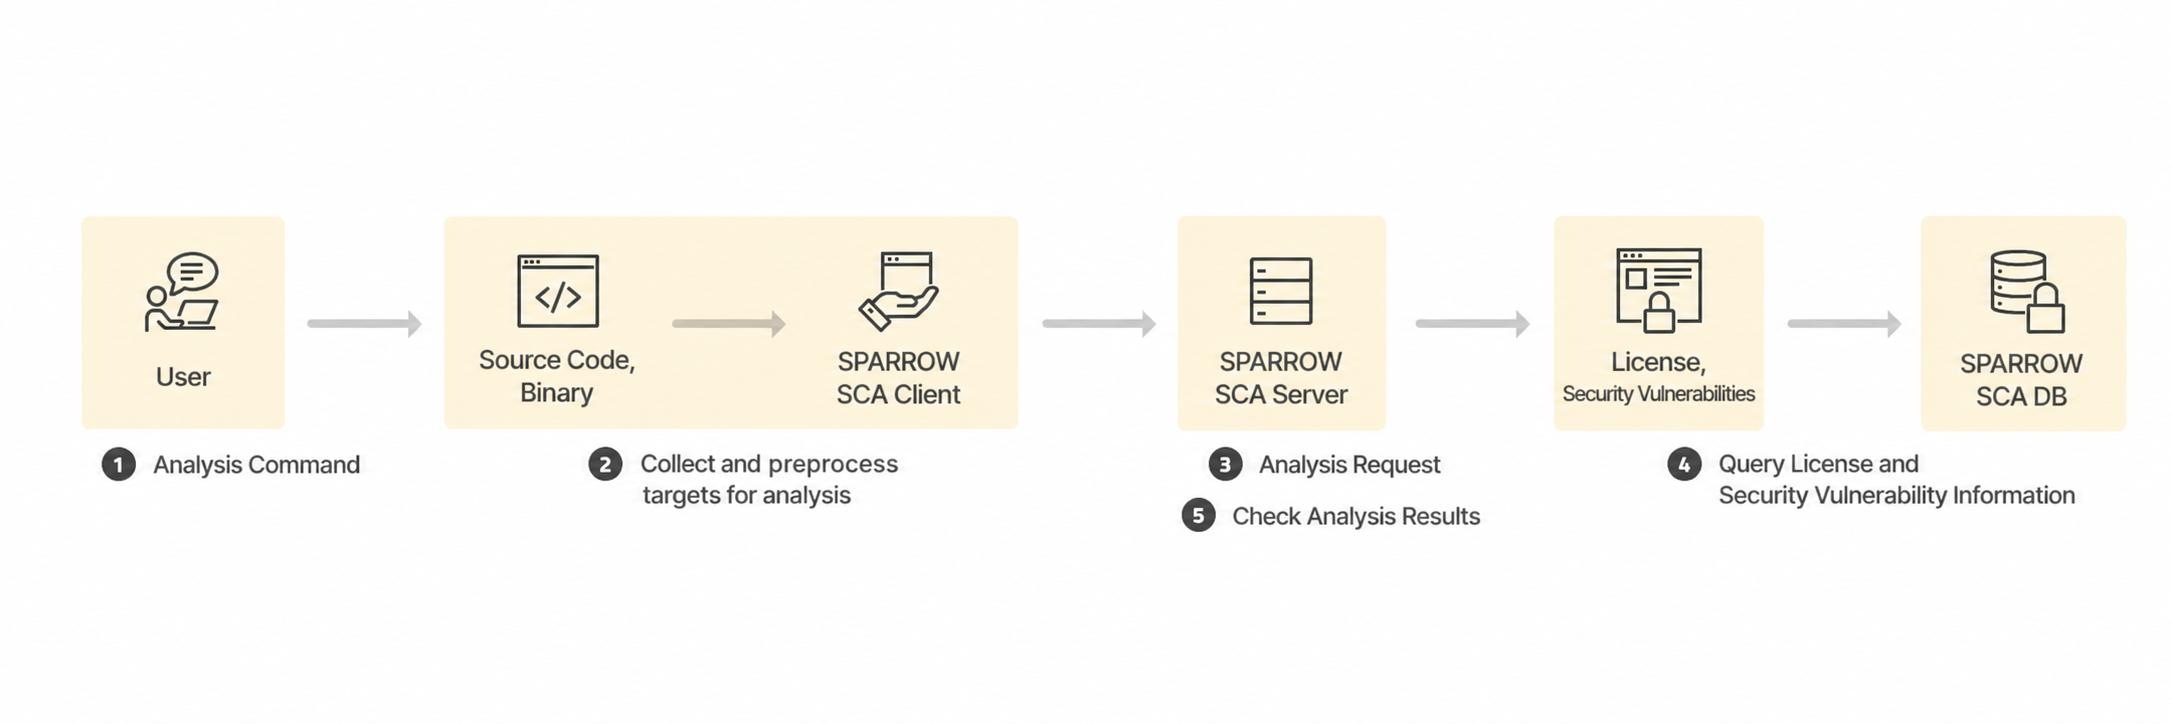
When a developer runs an analysis, the Sparrow SCA client collects the analysis targets, such as source code or binaries, and preprocesses them.
The Sparrow SCA server then identifies open source usage and security vulnerabilities based on its open source license and vulnerability database.
From the results, teams can review license risks and vulnerability status and take the necessary actions, such as updating to a secure version or fulfilling notice obligations.
FAQ
Q.
What are the benefits of adopting Sparrow SCA?
A
Sparrow SCA is an open source analysis and management tool. It enables efficient software supply chain management through SBOM generation, along with open source license identification and security vulnerability detection.
Q.
What is an SBOM?
A
An SBOM (Software Bill of Materials) is an inventory of the components in a piece of software that enables efficient supply chain management. Sparrow SCA can export SBOMs in formats including SPDX, CycloneDX, SWID tags, and NIS-SBOM.
Q.
What forms of open source software does Sparrow SCA support?
A
Sparrow SCA supports analysis of source code, binaries, dependency files, and code snippets.
Q.
Which compliance requirements can Sparrow SCA help me meet?
A
Sparrow SCA provides features to help you comply with the FDA cybersecurity guidance and software supply chain security guidelines.